
Your organisation, audit-ready and cyber resilient.
From information security and risk management to compliance. With more than ten years of hands-on experience, we guide you from your first assessment and implementation through to ongoing management.
PECB Trainings
Take an official PECB training in information security, risk management or AI. Standards such as ISO 27001, ISO 42001 and more. Choose classroom, virtual or e-learning.
Knowledge of the standards that matter
We know these standards inside out. We guide you through implementation and stand beside you during the audit.
NEN 7510
ISO 27001
EU AI ACT
DORA
BIO 2
AVG
Cbw (NIS2)
DigiD (Logius)
ISO 22301
ISO 27701
ENSIA
ISA/IEC 62443
Our focus areas
From insight to being in control
Assess
Start with insight
Before you can improve, you need to know where you stand. We test your organisation against the relevant standard or legislation and map out risks, gaps and priorities in concrete terms.
Implement
From insight to action
With the insights we have gained, we get to work. We translate the results into concrete measures, processes and documentation, aligned with the standard you are aiming for and with what works within your organisation.
Manage
Stay in control and grow
Already set something up, but lacking the attention or capacity to take it to a higher level? We support you in managing, measuring and improving your compliance programme on an ongoing basis, as a virtual CISO if desired.
Develop
Build knowledge in your team
Lasting resilience starts with knowledge. Through official PECB trainings, awareness programmes and webinars, we make sure your team gets the knowledge in-house to stay compliant.
Sectors we work in
Information security and compliance do not work the same way in every sector. Legislation, threats, technology and responsibilities differ. That is why we combine our Governance, Risk & Compliance (GRC) expertise with knowledge of the environment your organisation operates in.
Healthcare
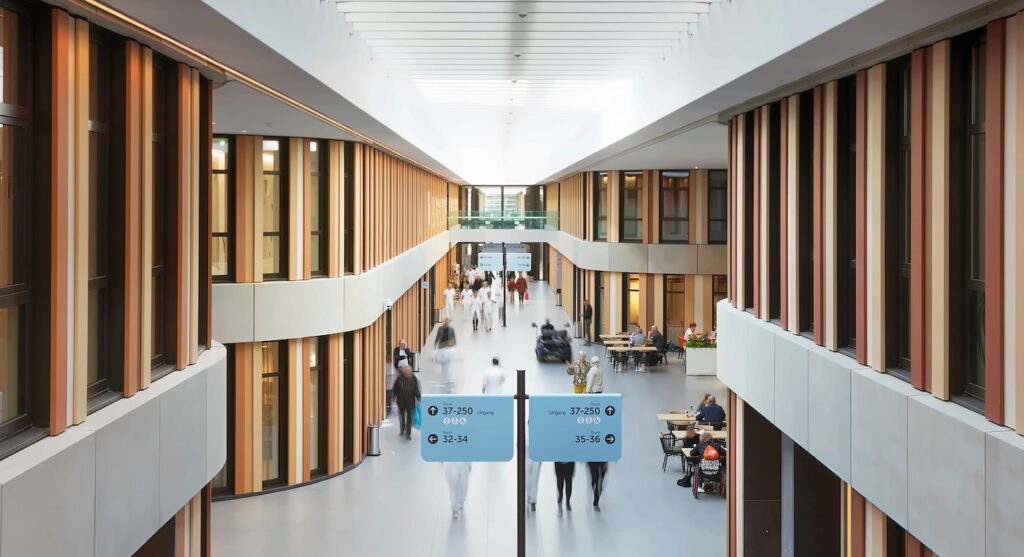
Healthcare deals with sensitive patient data, complex IT environments and strict information security requirements. We help healthcare organisations with, among other things, NEN 7510, NIS2 and DigiD. We know the sector inside out and help healthcare organisations become demonstrably compliant and resilient, without compromising the day-to-day delivery of care.
DigiD audit passed at Amphia Hospital through targeted file preparation and audit support
Amphia Hospital needed support to get the documentation and substantiation for the DigiD audit in order. ITS Risky focused on building the file, collecting the required evidence and preparing for the audit. This led to successfully passing the DigiD audit.
Amphia Hospital
Logistics
In logistics, goods flows, planning and systems must be available at all times. Because of the dependence on supply chain partners and suppliers, information security is a shared responsibility. We help logistics organisations with, among other things, ISO 27001, NIS2, the management of digital access and the control of supplier risks, so that security fits the operation and does not get in the way.
More control over digital access by linking Identity & Access Management to business processes
At DHL Parcel, digital access was relevant to the day-to-day execution of operational business processes.
ITS Risky worked on Identity & Access Management, with attention to the alignment between access management and business operations. As a result, the setup of digital access became part of the operational processes.
DHL Parcel
Public sector
Government organisations work with sensitive citizen data and must comply with fixed frameworks. We help municipalities and other public organisations with, among other things, BIO 2, DigiD and ENSIA, as well as technical information security and the control of supplier risks. This way, you gain verifiable control over information security within the frameworks you must comply with.
Technical ISO controls and supplier management strengthened within a municipal domain
The Municipality of Purmerend needed support with technical information security and the control of supplier risks within a domain. ITS Risky worked on technical ISO issues and supplier management. The assignment focused on strengthening control over, and insight into, the security of the environment concerned.
Municipality of Purmerend
Official PECB Partner
Through our PECB partnership, you get access to internationally recognised certification trainings in information security, privacy, AI, continuity and GRC. Practice-oriented and available for both individual professionals and complete teams.
- Internationally recognised certification
- Experienced, certified trainers
- Classroom, virtual or via e-learning
Featured PECB trainings
ISO/IEC 27701 Foundation
The ISO/IEC 27701 Lead Implementer training course equips professionals with the expertise to assist organizations in establishing, implementing, and continually improving a privacy information management system (PIMS) based on ISO/IEC 27701.
E-learning – 3 days
ISO 9001 Lead Auditor
The ISO 9001 Lead Auditor training course equips participants with the knowledge and skills needed to audit quality management systems (QMS) based on audit principles and best practices.
E-learning – 3 days
ISO 22301 Lead Auditor
The ISO 22301 Lead Auditor training course will equip you with the necessary competencies to audit business continuity management systems (BCMSs) based on best audit practices and principles.
Klassikaal – 3 days
ISO 37001 Foundation
The ISO 37001 Foundation training course provides participants with a comprehensive introduction to the fundamental concepts and requirements of an anti-bribery management system – ABMS based on ISO 37001:2025.
E-learning – 3 days
Frequently asked questions
Can’t find your question? Get in touch with us. We are happy to help!
What can ITS Risky do for our organisation?
We help your organisation become verifiably compliant and cyber resilient, from first assessment and implementation to ongoing management and knowledge development.
Through Assess, Implement, Manage and Develop, we meet you where you are today. You can start wherever your organisation needs it.
Does my organisation meet the requirements for information security?
Laws, regulations and standards such as ISO 27001, NEN 7510, NIS2/Cbw, DORA and the CRA place ever higher demands on information security and cyber resilience.
ITS Risky helps you gain insight into the obligations that apply to your organisation. With an assessment, we map the current situation, risks and areas for improvement. You get a concrete overview of what is already well in place and which steps are needed to be able to show that you are compliant.
What is the difference between ISO 27001 and NEN 7510?
ISO 27001 is an international standard for information security that is suitable for every sector. NEN 7510 is the Dutch standard for information security in healthcare.
It builds on ISO 27001 and adds requirements that apply specifically to healthcare, such as the handling of patient data. Which standard applies to you depends on your sector and the requirements of your clients.
How does ITS Risky help with achieving certification?
ITS Risky guides you from gap analysis through to implementation and audit preparation.
We also help translate relevant legislation, such as NIS2/Cbw and the CRA, into concrete measures.
This way, we make sure information security is not only right on paper, but also works in practice.
What is NIS2 and does it apply to our organisation?
NIS2 is a European directive that sets requirements for the cybersecurity of organisations in critical and important sectors. In the Netherlands, it has been transposed into the Cyberbeveiligingswet (Cbw), the Dutch Cybersecurity Act.
Whether the law applies to you depends on your sector and the size of your organisation. As a rule, it concerns medium-sized and large organisations. With an assessment or an introductory call, we determine together whether and how your organisation falls under it and what you need to do.
Do we need our own CISO, or can ITS Risky support us with this?
Not every organisation needs a full-time CISO. With a virtual CISO from ITS Risky, you get access to specialist knowledge and support with policy, risk management, compliance and legislation such as NIS2/Cbw, DORA and the CRA.
Even if your own CISO is temporarily absent, ill or on holiday, ITS Risky can take over the work and safeguard continuity.
This way, you stay in control of your information security.
Not sure where to start?
Whether you want to determine what NIS2, ISO 27001 or NEN 7510 mean for your organisation, or you already know exactly what support you are looking for: in a free introductory call we discuss where you stand and what a logical next step is.
Do you enjoy working on information security?
At ITS Risky, we keep the application process personal and approachable.